Ancient Cryptography: From Caesar's Cipher to Modern Cybersecurity and AI
From Caesar's battlefield codes to AI-powered encryption, cryptography has always been humanity's most consequential intellectual arms race. Discover how secrets shaped civilizations — and how they continue to shape our digital world.
Z(
Zara Maheem (Pakistan)
4 August 2026/9 min read
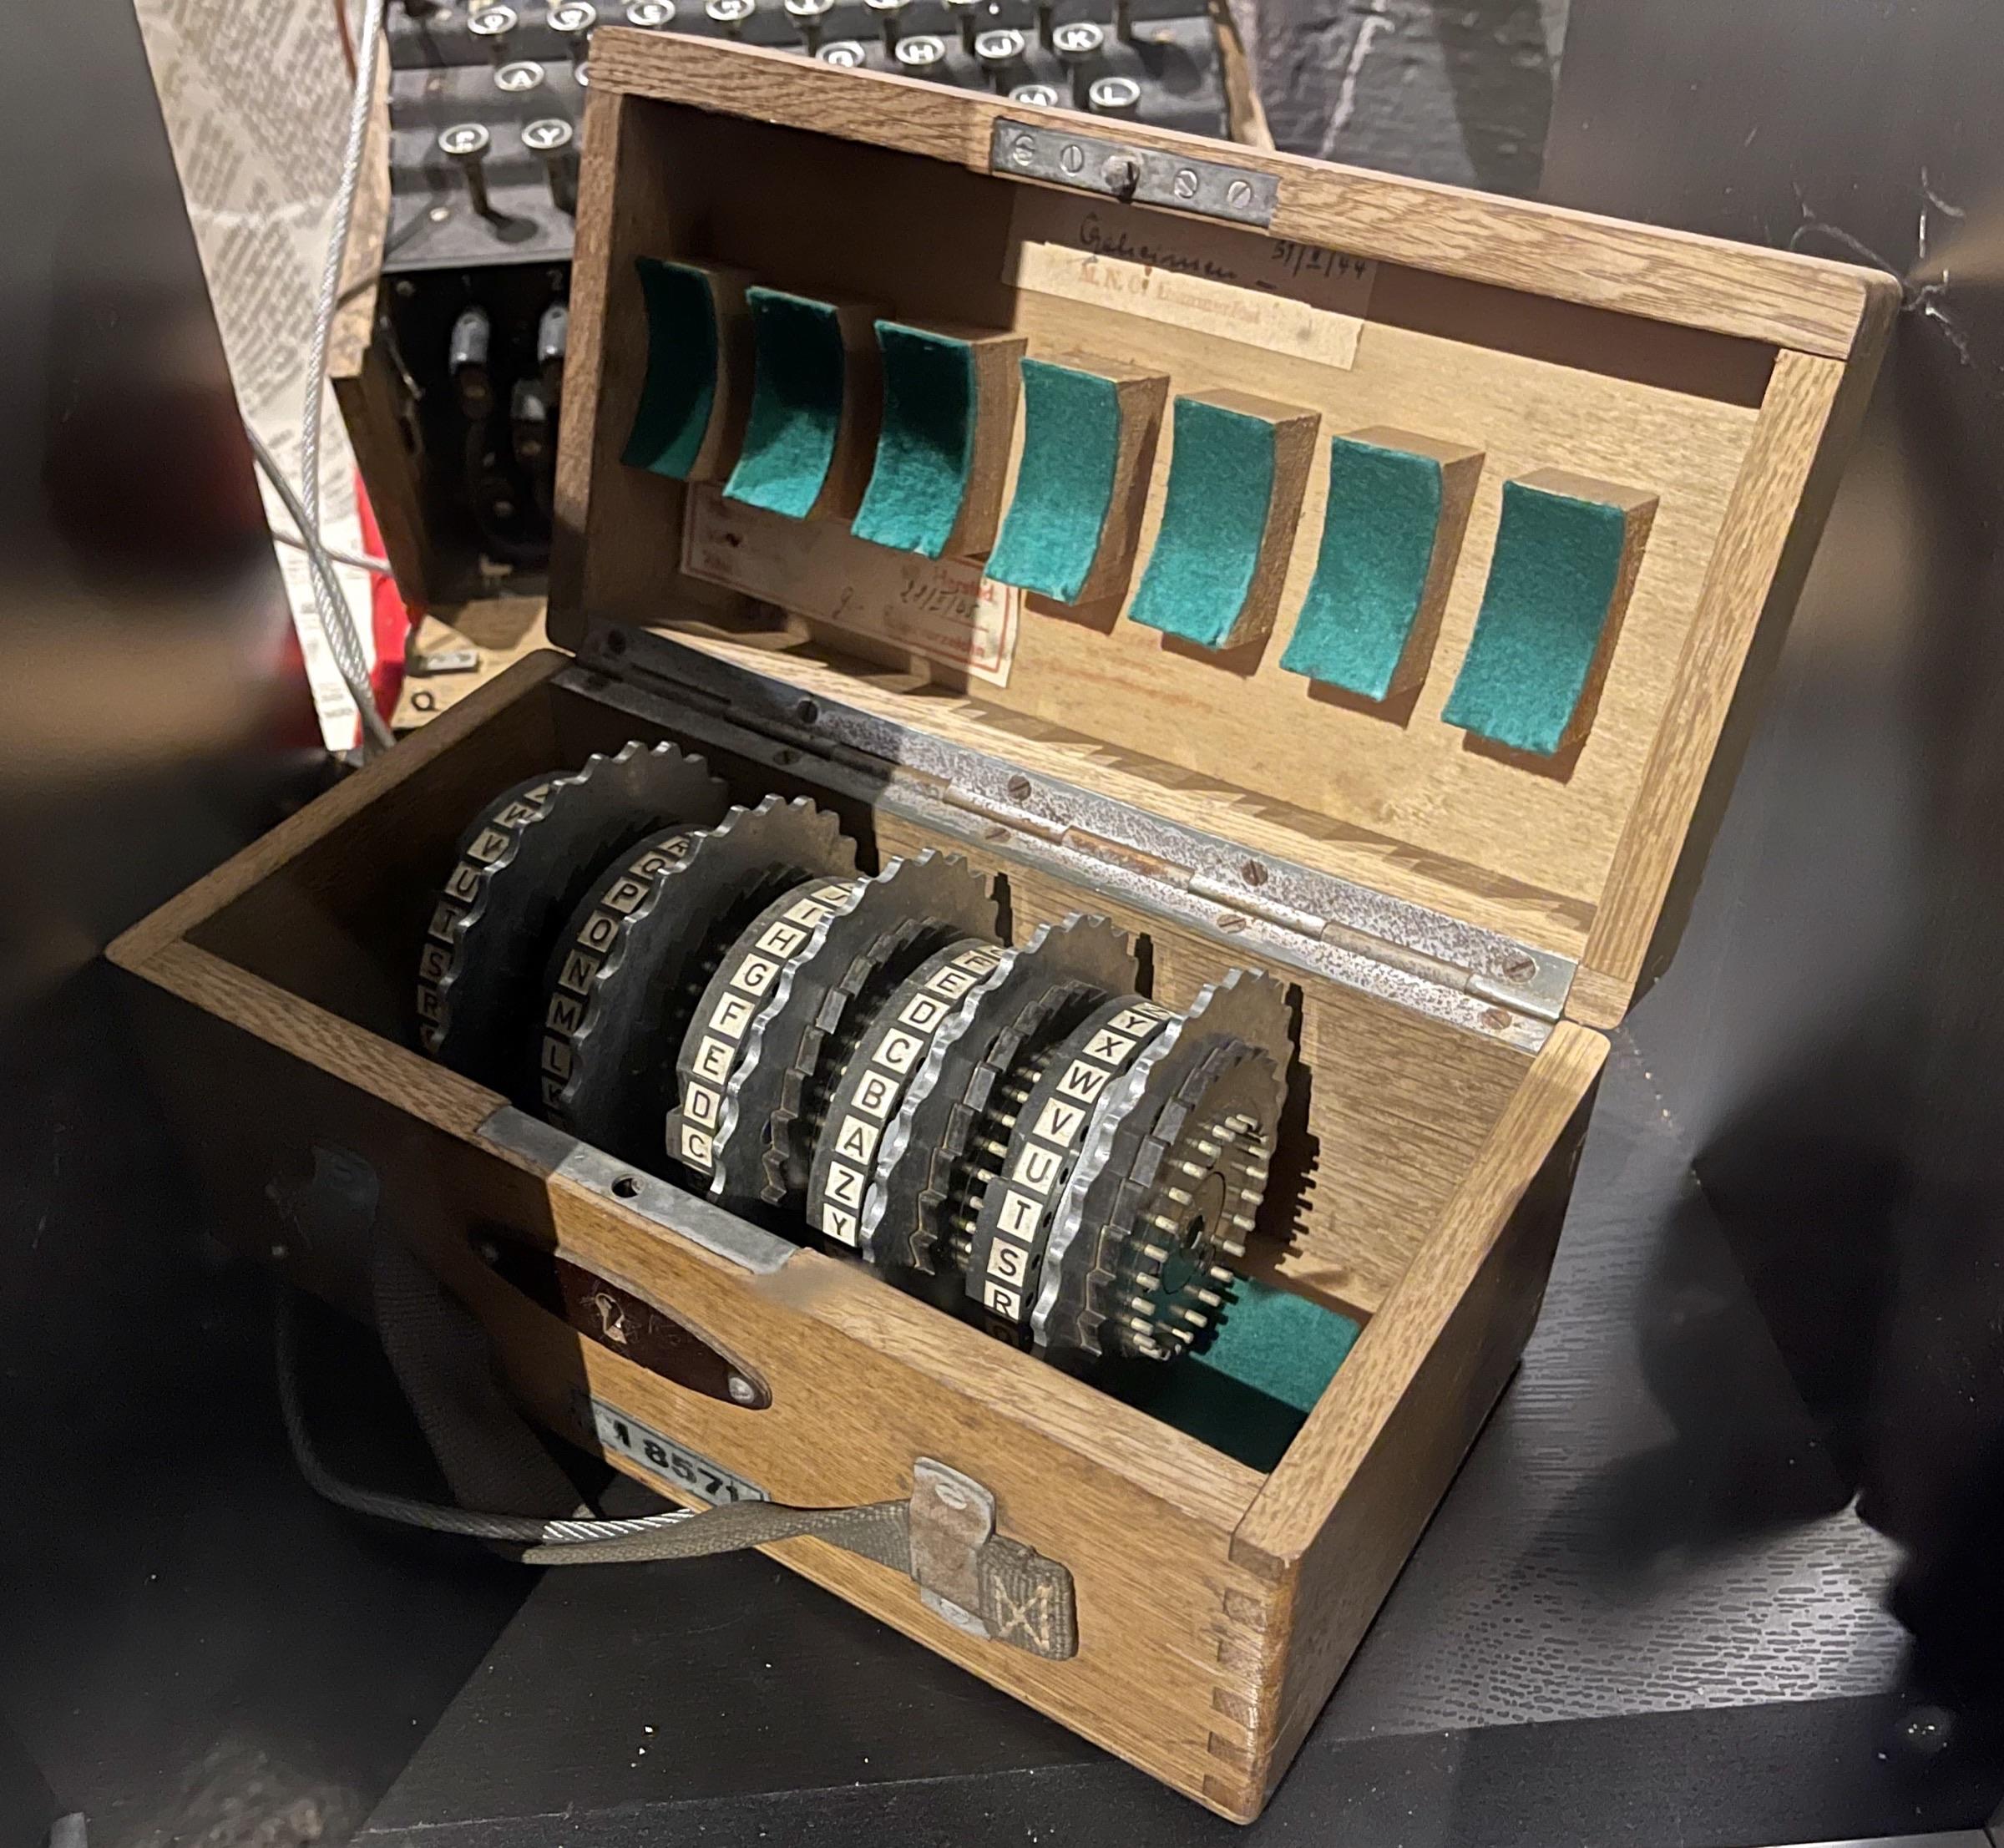
Enigma M4 rotor set in its case, Bergenhus Festningsmuseum, Bergen · Wolfmann · CC BY-SA 4.0
Secrets have always been at the heart of human civilization. Long before digital passwords and encrypted messaging applications existed, people devised ingenious methods to conceal their most important communications from enemies, rivals, and strangers. The history of cryptography — the science of encoding and decoding secret messages — stretches across thousands of years and dozens of civilizations, from the ancient Mediterranean world to the laboratories of modern artificial intelligence research. Understanding this history is not merely an academic exercise. It reveals something fundamental about who we are: creatures who simultaneously crave connection and fear exposure, who trust selectively and protect fiercely.
The journey from Caesar's simple cipher to today's quantum-resistant encryption algorithms is a story of escalation — each generation of cryptographers building something stronger, and each generation of codebreakers finding a way through. It is also a story of unintended consequences, of tools invented for secrecy that ended up shaping mathematics, computing, and the entire structure of the digital economy.
Caesar's Cipher: Simplicity as Strategy
The earliest encryption methods were elegant in their simplicity. Around 50 BCE, Julius Caesar developed what historians now call the Caesar Cipher: a substitution cipher in which each letter of the alphabet is shifted a fixed number of positions. Using a shift of three, the letter A becomes D, B becomes E, and so on through the alphabet. To read the message, the recipient simply shifts every letter back by the same number.
“Anyone can encrypt a message using the recipient's public key, but only the recipient, who holds the private key, can decrypt it.”
The Caesar Cipher worked not because it was mathematically sophisticated — it was not — but because it exploited a practical reality of the ancient world: most people could not read at all, and those who could read had no reason to suspect that a message in apparent gibberish contained hidden meaning. In an environment of widespread illiteracy, obscurity was its own form of security.
Yet even in ancient times, thoughtful observers recognized the cipher's weakness. If an intercepted message is known to be encrypted with a Caesar Cipher, a patient adversary needs only to test 25 possible shifts before finding the correct one. This brute-force vulnerability meant that the Caesar Cipher's effectiveness depended entirely on the enemy not knowing what kind of cipher was being used — a principle that later cryptographers would recognize as fundamentally flawed. Modern cryptography operates on the opposite assumption: a cipher should remain secure even when the enemy knows exactly how it works.
For centuries after Caesar, substitution ciphers remained the dominant approach to encryption. The standard method evolved beyond simple shifts into more complex systems in which each letter was replaced by a different symbol or letter according to a fixed but arbitrary key. These monoalphabetic substitution ciphers seemed to offer much stronger security, since the number of possible keys was astronomically large.
Then, in ninth-century Baghdad, a scholar named Al-Kindi changed everything. Working during the intellectual golden age of the Abbasid Caliphate, Al-Kindi wrote a treatise titled "A Manuscript on Deciphering Cryptographic Messages" in which he described a technique now known as frequency analysis. His insight was profound in its simplicity: in any language, certain letters appear far more frequently than others. In Arabic, for instance, some letters dominate ordinary prose. In English, the letter E accounts for roughly 13% of all letters used. If an encrypted text replaces every E with, say, the letter Q, then Q will appear with unusual frequency in the ciphertext — and a careful analyst can use this statistical signature to crack the code without knowing the key.
Al-Kindi's frequency analysis was a revolutionary intellectual achievement. It demonstrated that even a cipher with billions of possible keys could be broken by someone who understood the mathematical structure hidden within language itself. It also established a principle that remains central to cryptanalysis today: ciphers do not operate in a vacuum; they interact with the statistical patterns of human language and human behavior, and those patterns are exploitable.
The Renaissance and the Polyalphabetic Response
Al-Kindi's breakthrough forced cryptographers to adapt. The solution, developed across Renaissance Europe by scholars including Giovan Battista Bellaso and later popularized under the name of Blaise de Vigenère, was the polyalphabetic cipher. Instead of using a single substitution alphabet throughout a message, the Vigenère Cipher used a keyword to cycle through multiple different alphabets. Each letter of the keyword determined a different Caesar-style shift for the corresponding letter of the message. This cycling destroyed the simple frequency patterns that Al-Kindi's method exploited, because the same plaintext letter would be encrypted differently depending on its position relative to the keyword.
The Vigenère Cipher was considered unbreakable for nearly three centuries — so secure that it was called "le chiffre indéchiffrable," the indecipherable cipher. It was eventually broken in the 1800s through a technique that identified the repeating structure of the keyword by looking for repeated patterns in the ciphertext. Once an analyst determined the length of the keyword, the cipher collapsed back into a series of simpler Caesar ciphers, each breakable by frequency analysis.
This pattern — a new cipher, followed by the discovery of its weakness, followed by a stronger cipher — would repeat itself through the centuries with increasing speed and sophistication.
World War II: The Machine Age of Cryptography
The twentieth century brought both new powers of encryption and new powers of codebreaking. During World War II, Nazi Germany deployed the Enigma machine — an electromechanical cipher device that used a system of rotating rotors, a plugboard, and reflector elements to create an encryption scheme of staggering complexity. Each day, Enigma operators reset their machines according to a new daily key distributed in printed codebooks. The number of possible Enigma configurations ran into the quintillions. Breaking it by hand, letter by letter, seemed literally impossible.
But at Bletchley Park, a wartime codebreaking center in England, a remarkable collection of mathematicians, linguists, chess champions, and puzzle enthusiasts worked to do exactly that. Central among them was Alan Turing, a Cambridge mathematician who designed a machine called the Bombe specifically to exploit structural weaknesses in Enigma's operation. The Bombe could test thousands of possible configurations per minute, eliminating wrong answers through logical deduction and narrowing down the field to a manageable set of candidates.
Turing's work at Bletchley Park is credited with shortening World War II by an estimated two to four years. But its deeper significance lies elsewhere: in building a machine that could systematically test logical propositions at speed, Turing had laid the conceptual foundations for modern computing. The codebreaker and the computer were born from the same intellectual problem.
The Digital Revolution: Public Key Cryptography
The development of computers in the mid-twentieth century created both a crisis and an opportunity for cryptography. On one hand, computers could encrypt and decrypt messages far faster than any human, enabling much more complex ciphers. On the other hand, computers also made brute-force attacks vastly more powerful: a cipher that would take a human lifetime to crack could be broken in hours by a machine testing millions of keys per second.
The deepest conceptual problem, however, was not speed but logistics. All encryption systems up to that point were symmetric: sender and receiver had to share the same secret key before they could communicate securely. But how do you share a secret key over an insecure channel? You cannot encrypt the key using the same system it is meant to unlock. For centuries, this had meant that secure communication required physically transporting keys — a serious limitation for any large-scale system.
In 1976, mathematicians Whitfield Diffie and Martin Hellman published a paper proposing what seemed like a mathematical impossibility: a method by which two parties could establish a shared secret over a completely public channel, without ever having exchanged anything private. The solution relied on what mathematicians call a trapdoor function — a mathematical operation that is easy to perform in one direction but computationally infeasible to reverse without a specific piece of secret information.
The following year, Ron Rivest, Adi Shamir, and Leonard Adleman developed RSA, the first practical public-key cryptosystem. RSA exploits the mathematical relationship between multiplication and factorization: it is easy to multiply two large prime numbers together, but extraordinarily difficult to take a large composite number and determine what primes produced it. RSA generates two mathematically linked keys — a public key for encrypting messages and a private key for decrypting them. Anyone can encrypt a message using the recipient's public key, but only the recipient, who holds the private key, can decrypt it.
Public-key cryptography made the modern internet possible. Every secure website connection, every encrypted email, every online banking transaction relies on descendants of the mathematical insight that Diffie, Hellman, Rivest, Shamir, and Adleman developed in the 1970s. From Caesar's three-letter shift to RSA's mathematically intractable prime factorization, the evolution of encryption had traveled an extraordinary distance.
Artificial Intelligence and the New Cryptographic Frontier
Today, cryptography faces its most complex and multifaceted challenge yet: the simultaneous rise of artificial intelligence and quantum computing. Both technologies are transforming the landscape in ways that demand new cryptographic thinking.
Artificial intelligence has become a powerful tool for both attackers and defenders in the cryptographic arms race. Machine learning systems can analyze patterns in encrypted traffic — not breaking the encryption itself, but inferring information about the content from metadata such as timing, packet sizes, and communication patterns. AI systems can also automate sophisticated social engineering attacks, generating convincing phishing messages tailored to specific individuals, or exploiting human error rather than mathematical weakness.
On the defensive side, AI is being used to detect anomalies in network behavior that suggest an attack in progress, to automate vulnerability scanning, and to assist in the design of new cryptographic algorithms. Researchers are also exploring the use of neural networks in steganography — the art of hiding information within innocent-looking images, audio files, or text — creating channels of secret communication that are invisible not only to human observers but potentially to traditional detection software.
The more existential threat, however, comes from quantum computing. Quantum computers exploit quantum mechanical phenomena to perform certain calculations at speeds that make classical computers look stationary. The most significant cryptographic implication involves an algorithm called Shor's algorithm, developed in 1994, which can factor large numbers exponentially faster than any known classical algorithm. If large-scale quantum computers become practical, they would be able to break RSA and most currently deployed public-key cryptosystems in hours or days rather than the billions of years that classical brute-force methods would require.
In response, the global cryptographic community has spent the past decade developing post-quantum cryptography — encryption systems based on mathematical problems that appear to resist quantum attack. In 2024, the United States National Institute of Standards and Technology finalized the first post-quantum cryptographic standards, based on the mathematical hardness of problems involving lattices and hash functions. The transition to post-quantum cryptography is now underway, a process that will take years and affect virtually every computer system on the planet.
The Unending Arms Race
The history of cryptography is ultimately the history of an arms race that never ends. Every breakthrough in encryption is eventually followed by a breakthrough in cryptanalysis. Every new cipher creates new vulnerabilities; every new attack stimulates new defenses. What makes this race different from most is that the stakes grow higher with every iteration: where Caesar's cipher protected military orders, modern cryptography protects the medical records of billions, the financial infrastructure of nations, and the communication of dissidents living under authoritarian governments.
The lesson of cryptographic history is not that perfect security is achievable — it never has been, and probably never will be. The lesson is that security is a process, not a destination: a continuous negotiation between the power to conceal and the power to reveal, conducted in the language of mathematics, refined by the pressure of adversity, and shaped by the full complexity of human ingenuity. From Caesar's three-position shift to quantum-resistant lattice cryptography, that negotiation has never stopped — and shows no sign of stopping now.
Share
Z(
About the writer
Zara Maheem (Pakistan)
Zara Maheem (Pakistan) writes on history for The Aletheia.
The Aletheia Newsletter
Essays like this one, in your inbox.
One dispatch per issue. No noise, unsubscribe whenever.